ObsidioMESA

Resilience, explained.

Perspectives and practical guides on DDoS resilience, regulatory direction, and operational proof across the Middle East and Southeast Asia.
Shorter, bigger DDoS attacks: planning for the first minute
Perspective

November 2, 2026

Shorter, bigger DDoS attacks: planning for the first minute

NETSCOUT's 1H 2026 data shows high-capacity attacks up 1,286% and more attacks over within a minute. That puts the outcome on configuration, not people.

Read more →
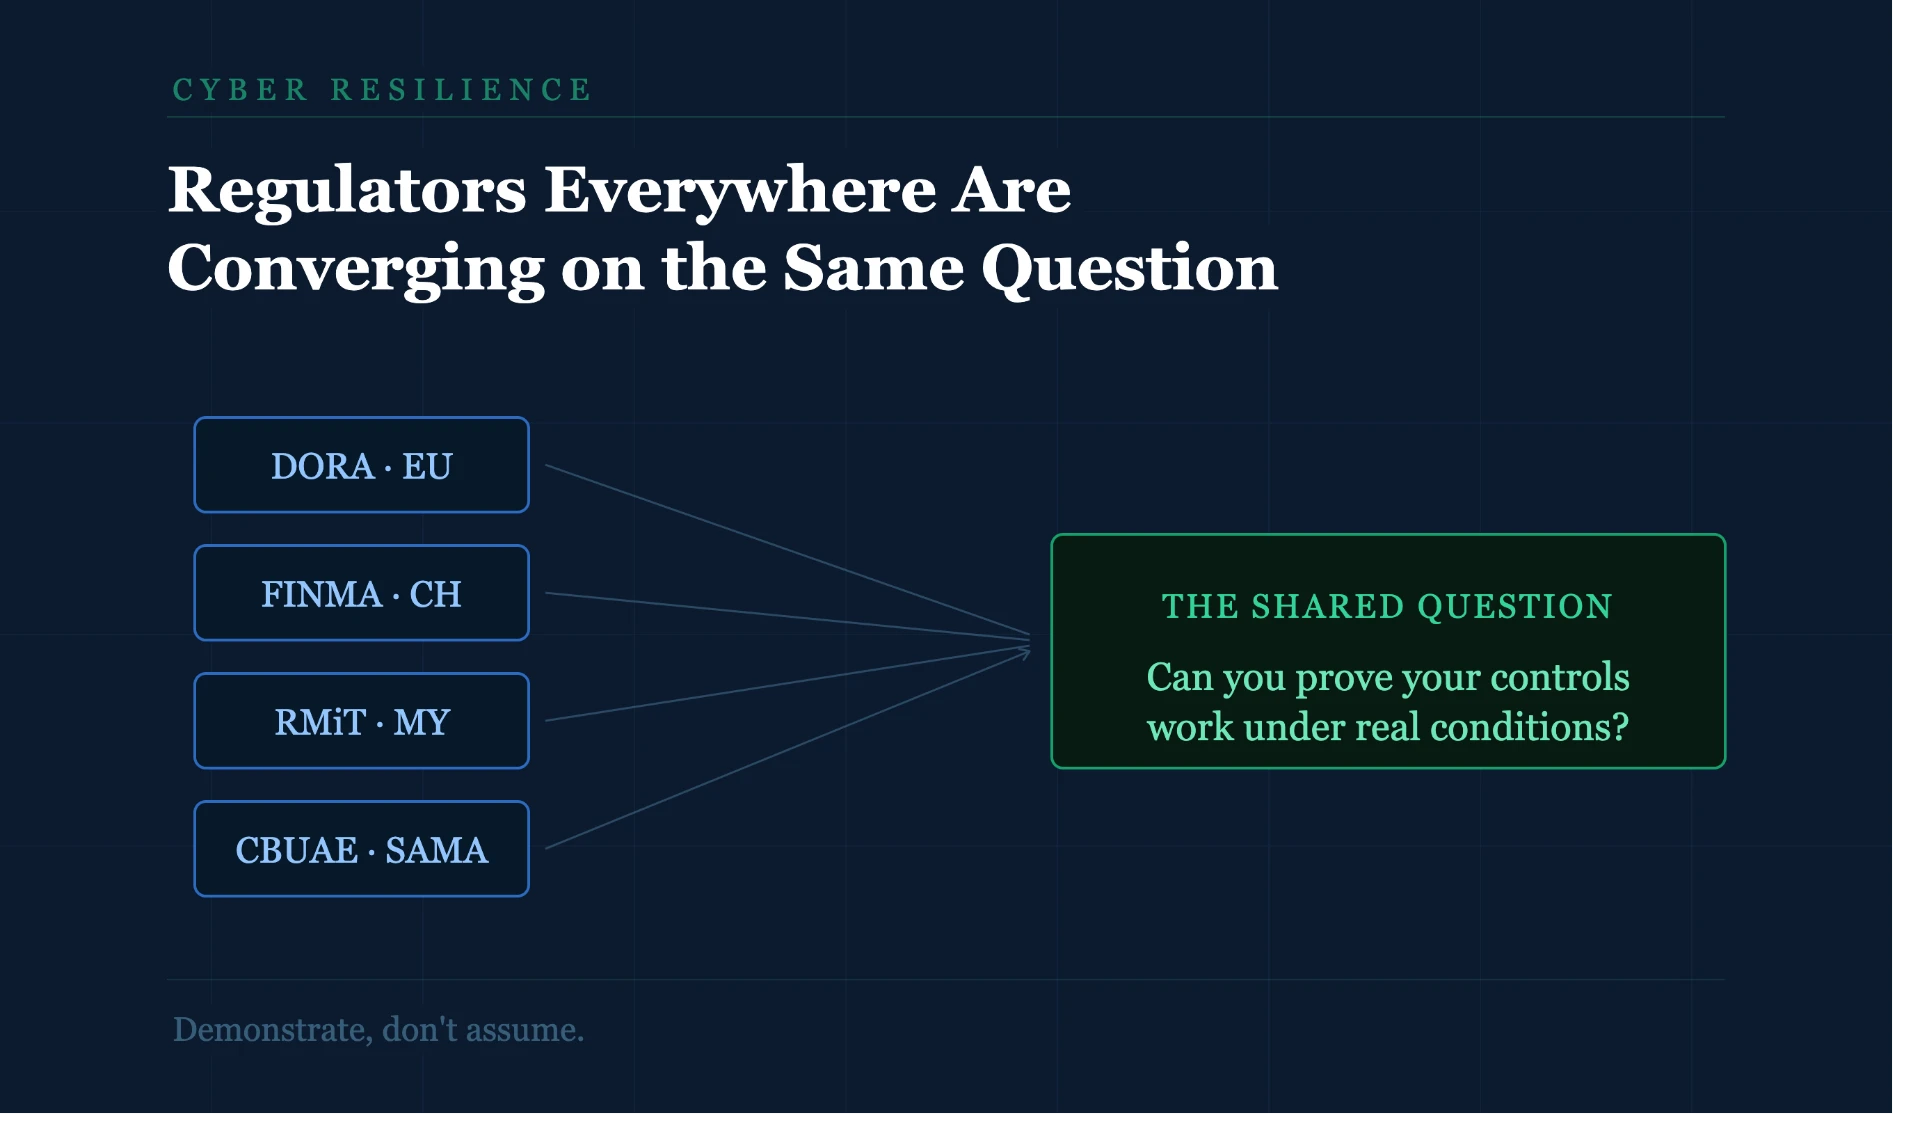
Regulators Everywhere Are Converging on the Same Question
Perspective

August 12, 2026

Regulators Everywhere Are Converging on the Same Question

DORA, FINMA, RMiT, and the Gulf frameworks look like a patchwork. Read them closely and they converge on one question: can you prove your controls work?

Read more →
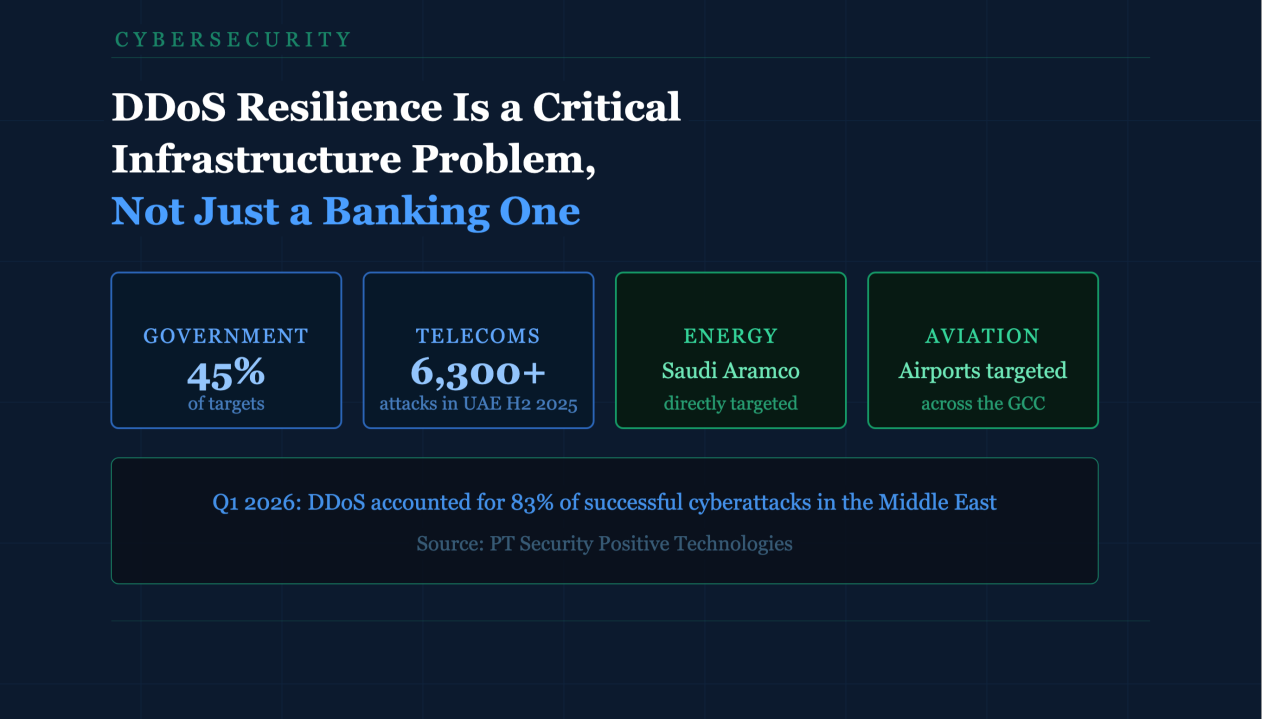
DDoS Resilience Is a Critical Infrastructure Problem, Not Just a Banking One
Perspective

July 30, 2026

DDoS Resilience Is a Critical Infrastructure Problem, Not Just a Banking One

The threat data no longer supports the assumption that DDoS risk belongs primarily to the financial sector.

Read more →
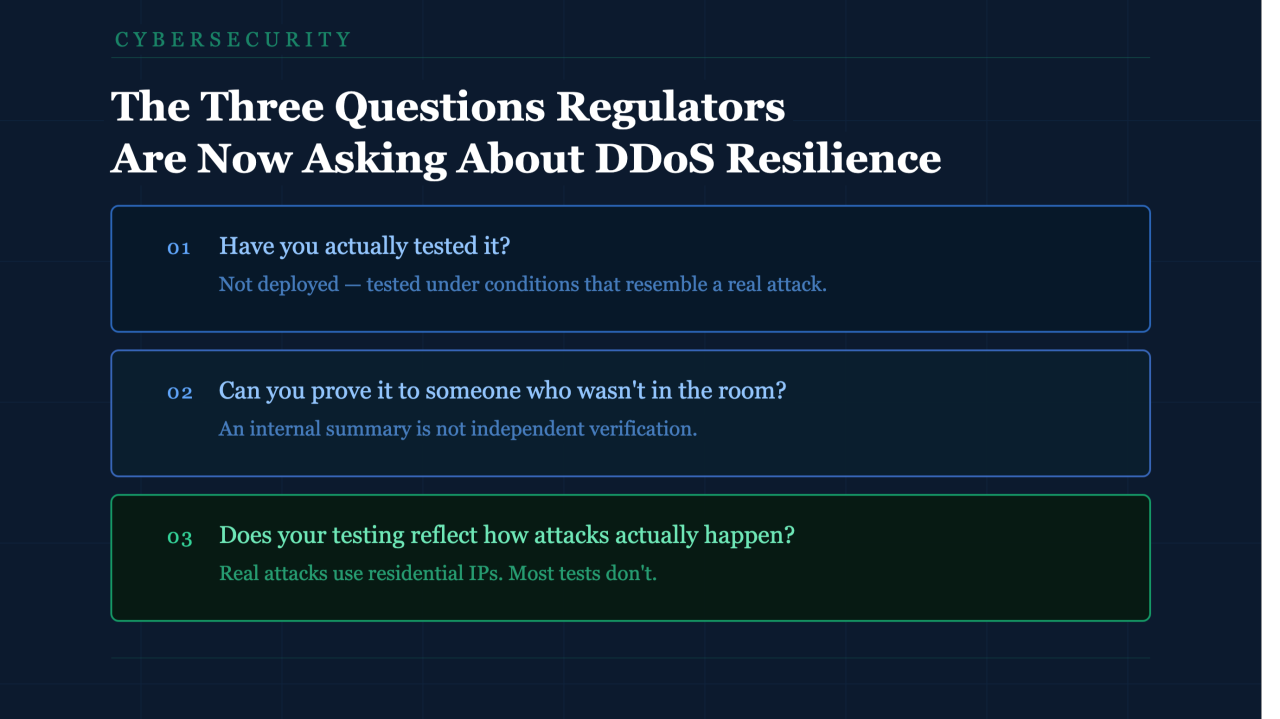
The Three Questions Regulators Are Now Asking About DDoS Resilience
Perspective

July 16, 2026

The Three Questions Regulators Are Now Asking About DDoS Resilience

The regulatory conversation has moved from whether protection exists to whether it has been tested, proven, and documented.

Read more →
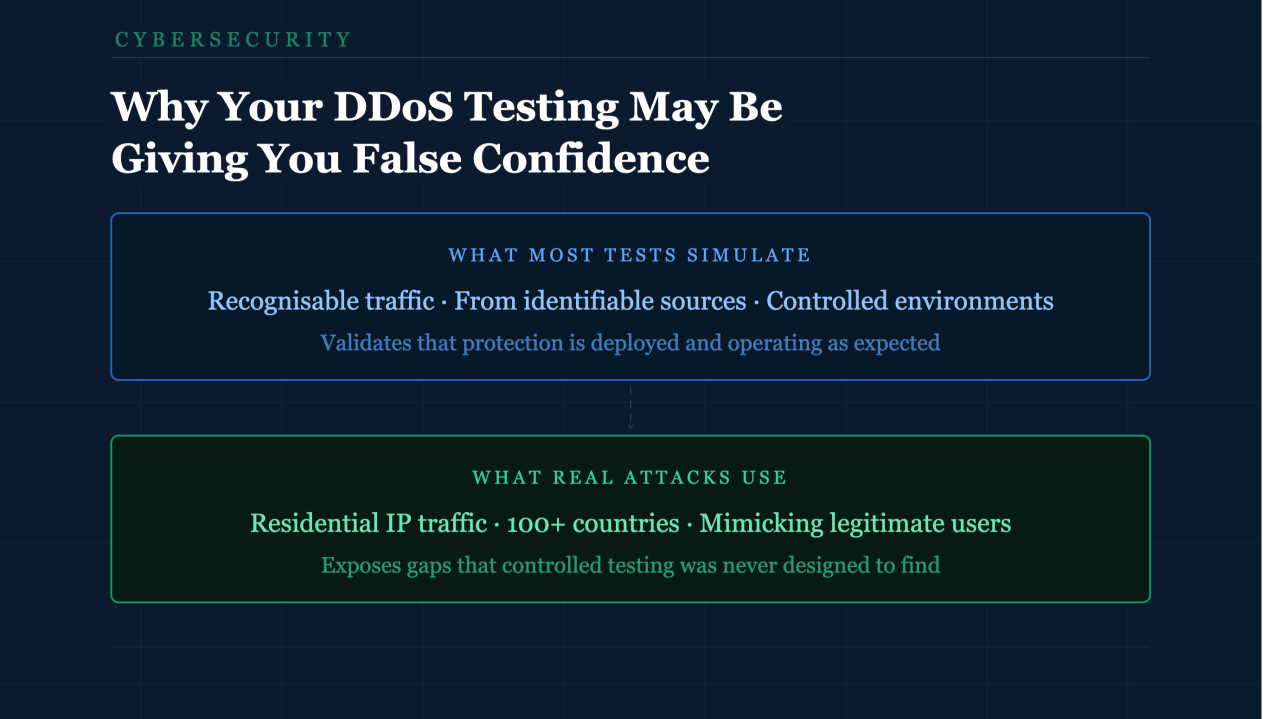
Why Your DDoS Testing May Be Giving You False Confidence
Perspective

July 2, 2026

Why Your DDoS Testing May Be Giving You False Confidence

A clean DDoS test can tell you your protection works and still leave you blind to how it holds up against the attacks actually hitting the market.

Read more →
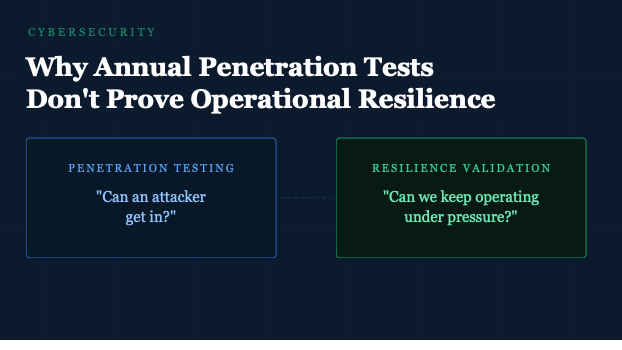
Why Annual Penetration Tests Don't Prove Operational Resilience
Perspective

June 18, 2026

Why Annual Penetration Tests Don't Prove Operational Resilience

Penetration testing tells you whether you can be breached. Resilience validation tells you whether you can keep operating if you are.

Read more →
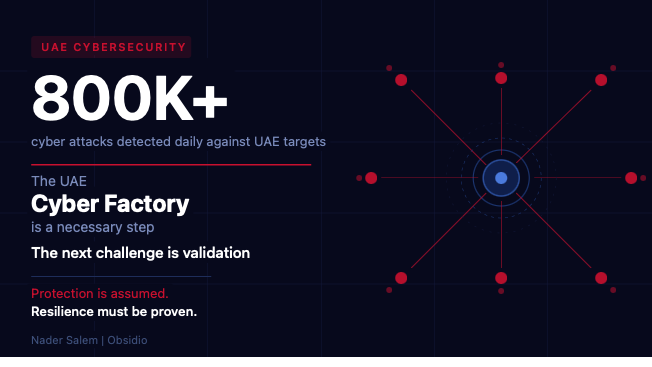
The UAE Cyber Factory Is a Necessary Step. The Next Challenge Is Validation.
Perspective

June 3, 2026

The UAE Cyber Factory Is a Necessary Step. The Next Challenge Is Validation.

National cyber defence capability is essential. Knowing the infrastructure it protects will perform under real attack is the next question.

Read more →
From Assumed Resilience to Demonstrable Resilience: The Next Evolution of Cybersecurity
Perspective

May 21, 2026

From Assumed Resilience to Demonstrable Resilience: The Next Evolution of Cybersecurity

There's a difference between having protection and knowing it works. That difference usually reveals itself at the worst possible time.

Read more →